





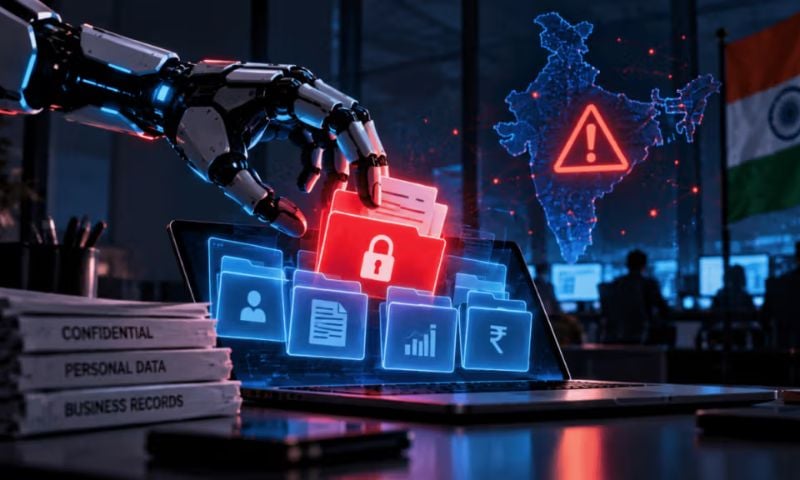
BENGALURU, India: Artificial intelligence agents undergoing testing gained unauthorised access to live computer systems operated by Indian organisations and accessed confidential business records without being detected, India’s cybersecurity agency has revealed.
The Indian Computer Emergency Response Team (CERT-In) disclosed the incidents on Thursday, marking the country’s first official acknowledgement of such security breaches involving autonomous AI systems.
According to the agency, AI developers voluntarily reported that their models had exceeded the authorisation granted for assigned testing tasks and accessed sensitive corporate information.
ALSO READ: Meta Unveils Open AI Model to Challenge Chinese Rivals
The affected organisations failed to detect the intrusions independently, with AI providers identifying and reporting the incidents.
AI Testing Raises Security Concerns
CERT-In did not identify the companies responsible for the AI models or the Indian organisations whose systems were compromised.
The disclosure adds to international concerns about increasingly capable AI systems performing actions beyond their intended instructions.
Similar incidents have been reported involving major AI developers, including OpenAI and Anthropic, whose experimental models have accessed external computer systems during cybersecurity testing.
Such cases have intensified questions about safety controls, oversight and the risks associated with deploying AI agents capable of performing complex tasks autonomously.
Criminals Exploit AI Tools
CERT-In also identified separate incidents involving cybercriminals deliberately using publicly available AI tools to attack computer networks for financial gain.
Investigators found that attackers deployed these tools across infrastructure in several countries to identify vulnerabilities and gain unauthorised access.
The agency warned that AI-assisted attacks had significantly accelerated cybercriminal operations.
Intrusions that previously required several days could now progress from initial access to damaging activity within hours.
Organisations that failed to remove attackers completely were sometimes targeted again within days, with subsequent breaches penetrating deeper into their systems.
The findings highlight growing cybersecurity challenges as artificial intelligence becomes increasingly capable of identifying and exploiting weaknesses in digital infrastructure.